Custom software for digital banks, lending platforms, credit unions, and fintech companies, with banking AI (fraud detection, credit risk scoring, document extraction, automated regulatory reporting) built into the architecture, not added after.
We build the technology layer that banking products run on, from customer-facing digital banking apps to the backend systems that process transactions, manage compliance, and automate operations.
Banking AI for fraud detection, credit risk scoring, document extraction, and automated regulatory reporting
Digital banking applications, account management, payments, statements, and customer self-service
Lending origination, underwriting automation, and loan servicing platforms
Payment infrastructure with payment gateway integrations and transaction processing
The problem
Sound familiar?
Running banking operations on legacy core systems that can't support the digital products your customers expect?
Building a lending or payments product and need software that meets compliance requirements without sacrificing speed to market?
Short answer
RaftLabs builds banking AI and custom software for digital banks, lenders, credit unions, and fintechs: fraud detection at transaction time, credit risk scoring with custom ML models, document extraction for loan origination, and automated regulatory reporting, alongside digital banking apps, lending origination and servicing, payment infrastructure, and KYC/AML tooling. PCI-DSS and KYC/AML rules are designed into the architecture before any code is written, and banking AI is built with the documentation regulators expect, not a black box. Teams typically launch a validated v1 in 10 to 16 weeks at a fixed cost, then iterate.
Trusted by
Banking software that compliance teams can ship
Banking software has two hard requirements that most software doesn't. It has to work reliably at the transaction level (financial errors aren't acceptable), and it has to satisfy the compliance and audit requirements that regulators impose.
Both requirements have to be designed in from the start, not retrofitted after the product is built.
01 Diagnosis
Where banking software usually breaks
01
Problem
A bad experience with a core processor
Solution
Gather a group of community bankers and you'll quickly find their common ground: a bad experience with a core processor. Lack of responsiveness. Steep conversion or deconversion fees. Brutal terms to terminate a contract early. The exclusivity clause has near total control over your destiny for the next 5, 7, or 10 years, unless you're prepared to cough up 50%, 80%, or even 100% of the remaining contract value to exit. Meanwhile compliance teams spend weeks manually extracting data from disparate systems to produce BSA, FinCEN, or open banking reports. Every manual step adds cost and introduces the risk of errors that regulators notice. We build compliance tooling into the product architecture so reporting is automated and auditable from day one. The outcome is compliance that doesn't eat margin.
02
Problem
We can do it in 5 years, and you will have to pay XXX million
Solution
A new savings product or loan type requires months of core system changes, IT sign-off cycles, and vendor involvement. By the time the product is live, competitors have already captured the market. The core becomes a constraint on commercial decisions rather than infrastructure that enables them. One banker put it plainly: they asked their core provider for what customers demanded and got back, we can do it in 5 years, and you will have to pay XXX million to us to do it. We build an API layer over the existing core so digital products can launch without waiting for the core to change. The outcome is products that ship before competitors capture the market.
03
Problem
The switching cost becomes architectural
Solution
The switching cost stops being a line item and becomes architectural. One credit union stayed with the same legacy core for 26 years, not because anyone liked the product. Integrations depended on the core, workflows depended on those integrations, and years of other vendors sat layered on top. Identity verification and transaction monitoring handled by staff takes days per customer and creates inconsistent results. Manual KYC processes don't scale and they don't satisfy auditors who want a documented, repeatable workflow. We integrate KYC and AML tooling directly into the product so every check is automated, logged, and auditable. The outcome is onboarding that scales without the manual tax.
04
Problem
They will abandon rather than get something wrong
Solution
In customers' minds, the application is like a test. People feel like they have to get it right, because if they don't, you might deny them the account or the loan. They will abandon rather than get something wrong. Meanwhile batch fraud review catches fraudulent transactions hours after they clear, when recovery is difficult or impossible. The longer the detection latency, the larger the loss exposure. We build fraud detection that runs at transaction time, using configurable rule sets and anomaly detection so suspicious activity is flagged before it settles. The outcome is applications customers finish and fraud caught before it settles.
02 What we ship
Banking software we build
01
Banking AI and automation
Banking AI features: credit risk scoring with custom ML models, fraud detection and anomaly detection, document extraction for loan origination (income verification, bank statement analysis), automated customer support for banking queries, and automated regulatory reporting. This is the same capability described above under the fraud, KYC/AML, and compliance-reporting problems we solve: real-time anomaly detection instead of batch review, and automated report generation instead of a manual extraction cycle. Banking AI requires explainability for regulatory reasons, so we build models with documentation adequate for compliance review, not black-box systems your regulators won't accept. The outcome is AI your examiners can review.
02
Digital banking applications
Customer-facing banking apps with account dashboards, transaction history, fund transfers, payment initiation, statement downloads, and customer service integration. Mobile-first for the customers who don't visit branches. Includes secure authentication (biometrics, OTP, step-up auth for high-value transactions), session management, and device fingerprinting, so your customers transact with confidence and your security team can sleep at night. The outcome is digital banking customers finish.
03
Lending origination and servicing
Digital lending platforms covering application intake, document collection, automated underwriting with credit bureau integration, decisioning workflows, disbursement processing, repayment tracking, arrears management, and customer communications. The bottleneck in commercial lending isn't intelligence, it's logistics: keying numbers from tax returns into spreadsheets, reconciling discrepancies between P&Ls and bank deposits. We automate the mechanical work so analysts spend time on credit quality. Regulatory compliance for Truth in Lending, Equal Credit Opportunity Act, and state lending regulations is built into the workflow design. The outcome is lending where analysts analyze.
04
Payment systems and infrastructure
Payment processing infrastructure: payment gateway integrations (Stripe, Adyen, Braintree), ACH and SWIFT payment flows, card program management, FX and multi-currency handling, and merchant payment platforms. Includes payment reconciliation, settlement, and chargeback management. PCI DSS compliance requirements are considered in the architecture from day one, so you don't carry certification debt into production. The outcome is payments without the certification debt.
05
KYC, AML, and compliance tooling
Compliance infrastructure for regulated banking products: KYC workflows with document verification (Jumio, Onfido, or similar), identity verification, sanctions screening, PEP checks, and ongoing monitoring. AML transaction monitoring with configurable rule sets and case management. SAR filing workflows and audit trail generation. Regulatory reporting for BSA, FinCEN, and international equivalents. Compliance tooling is built into the product rather than bolted on, so auditors see a system that was designed to comply, not one that was patched to comply. The outcome is audits that pass.
06
Core banking modernization
Modernizing legacy core banking systems without stopping the bank. We build an API layer over existing core systems to enable digital products while the core is gradually replaced. New products run as microservices, independent of the legacy core. Data migration from legacy formats includes reconciliation and audit. We assess the existing system before recommending the modernization approach, so the plan fits your infrastructure rather than a generic playbook. The outcome is modernization without the root canal.
03 Buy, build, or wait
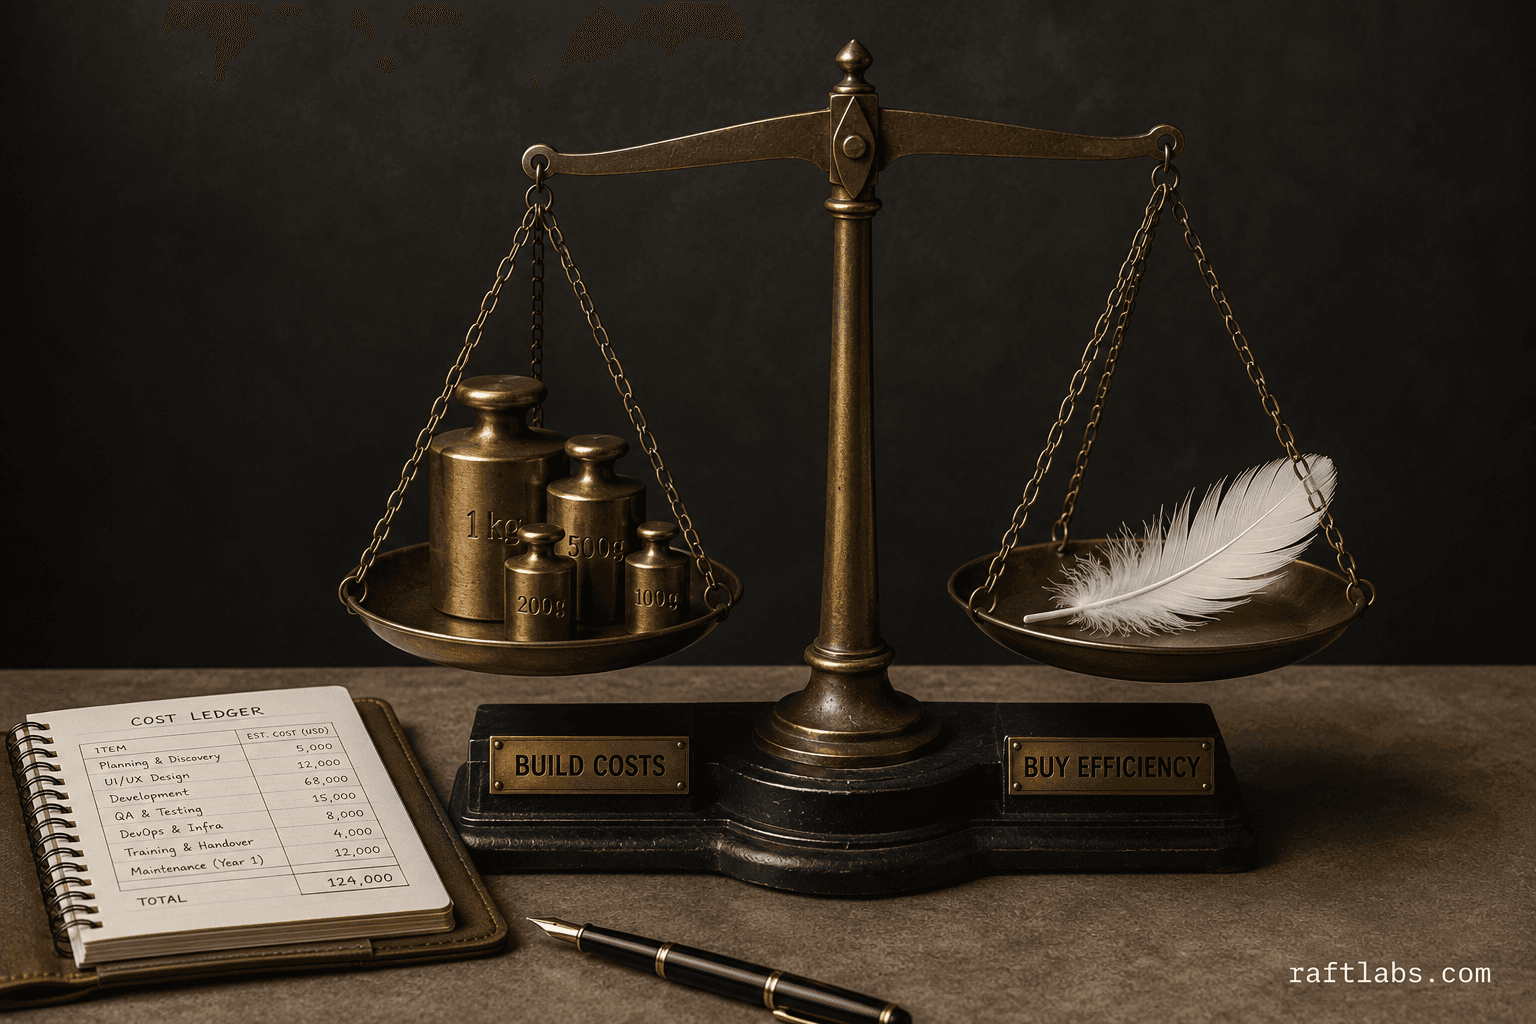
The banking software decision is usually about the core: what it allows, what it charges, and what it delays.
Stay on the core
FIS, Fiserv, Jack Henry
When the system handles your products and the vendor relationship works.
Build custom
When the core quotes 5 years and XXX million
What customers demand shouldn't wait on the vendor's roadmap. An API layer breaks the pattern.
When the switching cost is architectural
26 years on a legacy core nobody liked. Build the products the core can't ship.
When lending is a logistics problem
The bottleneck isn't intelligence, it's re-keyed data. Automate the mechanical work.
Bottom line
Stay on the core while it fits. Build when the core owns your roadmap or your margins.
04 How we work
How we work with banking clients
01
Compliance and technical discovery
We start by mapping your regulatory environment: PCI-DSS, KYC, AML, open banking, and any jurisdiction-specific requirements, alongside your existing core banking infrastructure. We identify what the core exposes via API, what requires workarounds, and where compliance constraints shape the architecture. You get a scoped proposal and a fixed cost before development starts. The risk this retires: the integration the core vendor wouldn't document.
02
Architecture design with compliance built in
Banking software architecture decisions have compliance consequences. We design data models, access control structures, encryption, audit logging, and infrastructure configuration to meet your regulatory requirements before any code is written. Your compliance team reviews the architecture document before development begins. The risk this retires: the requirement the examiners found first.
03
Sprint-based development with working software each cycle
We build in two-week sprints. At each sprint review you see working software you can test, not a slide deck of what's coming. Compliance-critical components are tested against your requirements at each sprint, not deferred to a final QA phase where fixing problems is expensive. The risk this retires: the compliance gap discovered after launch.
04
Security testing, launch, and handover
Before go-live, we conduct penetration testing and a security review against your requirements. We provide full technical documentation, run onboarding for your team, and support the production deployment. You own the infrastructure and the full technical documentation. The risk this retires: the vulnerability the pentest found first.
Across dozens of industries, we recognise your situation fast, then frame the fix around your margin and your operations, not a generic template.
02
We own the number, not the ticket
We measure success the way you do: hours saved, revenue earned, margin recovered. We stay through launch and growth, so the result is ours to own.
03
Serious businesses trust us
Vodafone, T-Mobile, Cisco, Energia, Aldi, Nike. Building since 2015. Serious businesses keep coming back because we stay accountable long after launch.
09 Questions
Common questions
Fraud detection that runs at transaction time using configurable rule sets and anomaly detection, so suspicious activity is flagged before it settles rather than caught in batch review hours later. Credit risk scoring with custom ML models. Document extraction for loan origination: income verification and bank statement analysis. Automated regulatory reporting for BSA, FinCEN, and international equivalents. Banking AI needs to be explainable for regulatory reasons, so we build models with documentation adequate for compliance review, not black-box systems your regulators won't accept.
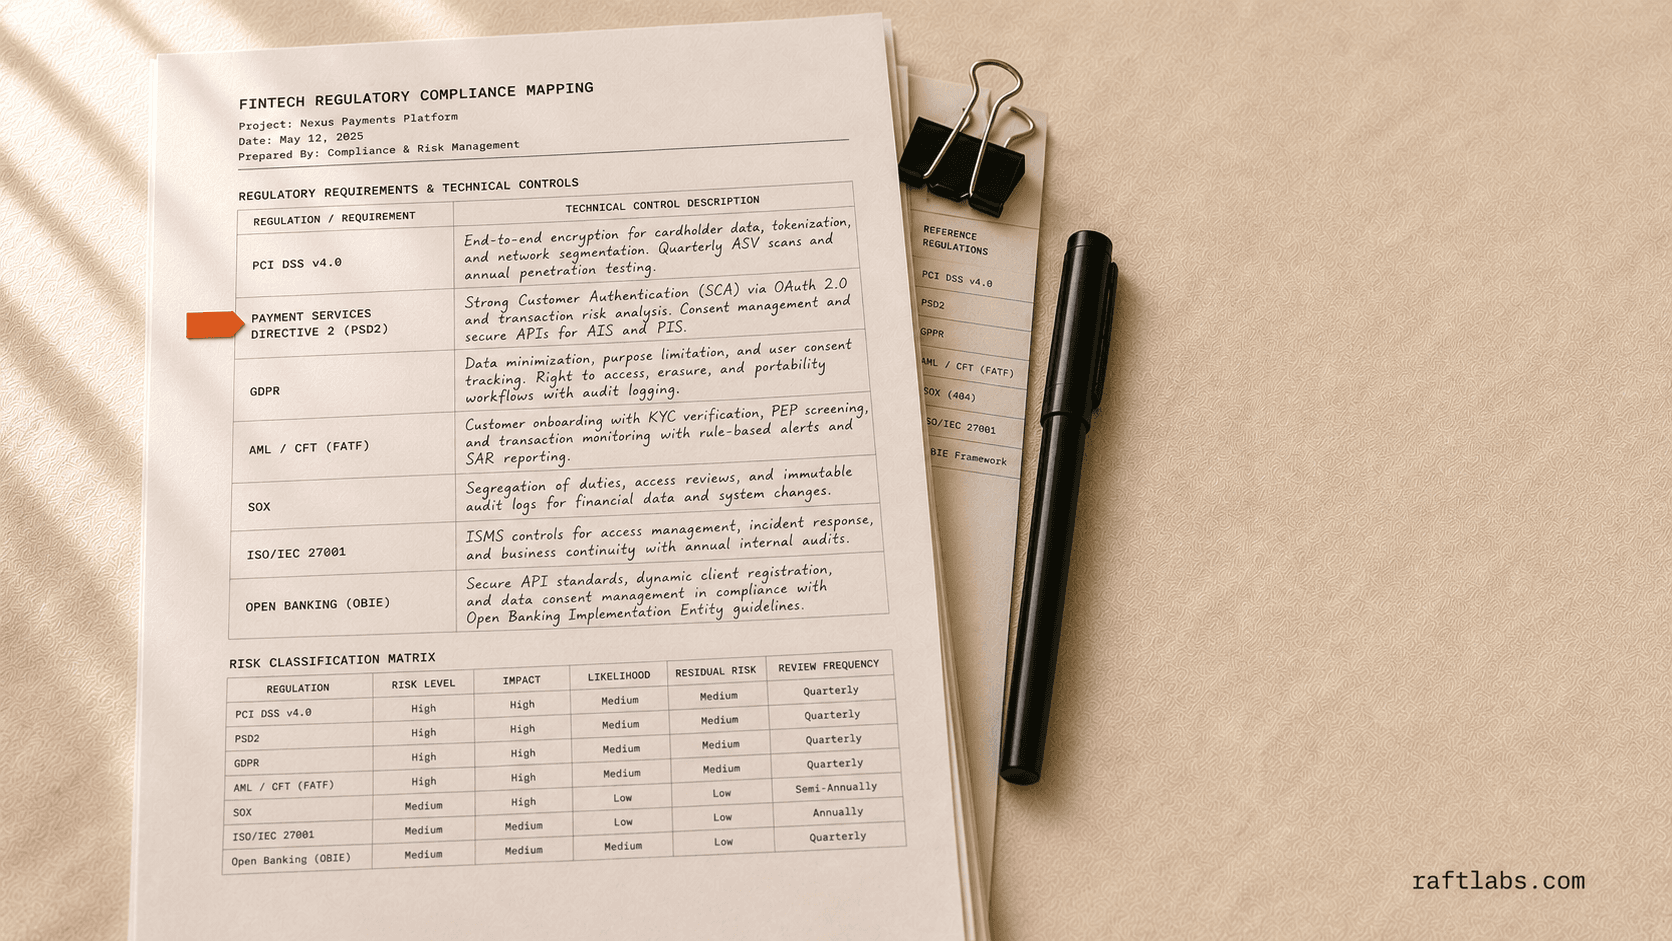
Requirements vary by product type and jurisdiction. Card systems need PCI DSS. Transaction monitoring and suspicious activity reporting fall under BSA/AML, and customer onboarding needs KYC. Customer data is governed by GDPR and CCPA, cloud-hosted infrastructure by SOC 2 Type II readiness, and API-based integrations by open banking and PSD2 standards. We engage your compliance team in discovery. Compliance shapes the architecture, not the other way around.
Yes. Most banking software projects involve integration with an existing core banking system (Temenos, FIS, Fiserv, Jack Henry, or a proprietary legacy system). Integration approaches depend on what the core exposes: modern cores have REST APIs; older systems expose SOAP, FTP-based file exchange, or direct database connections. We assess the integration surface during discovery. The most common pattern is an API layer that abstracts the core, allowing digital products to evolve independently while the core remains stable.
We treat security requirements as architectural constraints, not post-build additions. That means encryption at rest and in transit for all financial data, role-based access control with least privilege, and MFA plus step-up authentication for sensitive transactions. It also means full audit logging of who accessed what and when, penetration testing before launch, OWASP-aligned development with dependency scanning and secrets management, and infrastructure hardening for production.
We build payment processing systems, PCI-DSS-scoped fintech products, and banking-adjacent applications for financial services clients. One example is a mobile point-of-sale platform for a UAE fintech operator that processed over 10,000 transactions in its first three months. Every financial services project treats compliance and data security as baseline constraints, not optional extras.
BaaS providers handle the regulated infrastructure layer well for standard products: accounts, ledger, payment rails. Custom software makes sense in three cases. The product experience, credit model, or workflow is specific enough that BaaS configuration creates friction. You need to own the full stack for competitive or compliance reasons. Or per-transaction economics don't work at your volume. We scope both options during discovery and tell you which approach fits your situation.
Most teams launch a validated v1 of a digital banking feature set in 10 to 16 weeks, then iterate from there. The full product is an ongoing build. We agree a fixed cost before development starts, with milestone-based payments. Cost depends on scope and compliance complexity, and core banking modernization is scoped separately from a digital product build.
That fear is common and honest. Tellers and loan officers on legacy interfaces need retraining, and retraining cost is the moat that keeps banks on bad systems. We design the staff workflows with the people who run them. Interfaces that match how they already serve customers, not how a vendor thinks they should. The system ships when your frontline team can run a full business day on it without help.