AWS Migration Services
AWS migration services for workloads that need an owned landing zone before they need more services.
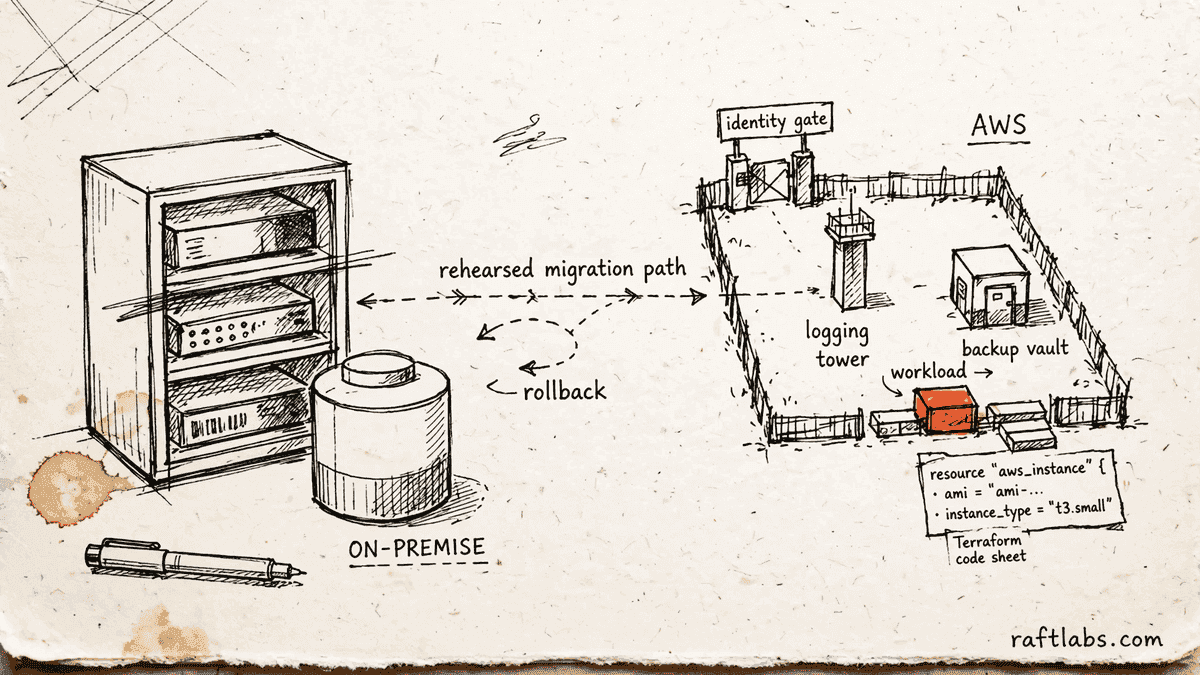
An AWS migration starts with account, identity, network, logging, backup, and cost boundaries. We map dependencies, choose a rehost or replatform path per workload, define the environment as code, rehearse the cutover, and validate the application before the source retires.
Bring the problem, the current workflow, or the existing code. We reply with a practical next step within one business day.
The brief
Start with what is not working.
Good software decisions begin with the constraint, not a list of features or a preferred technology.
Is the team selecting EC2, ECS, Lambda, or EKS before it has mapped workload behavior and operating capacity?
Would copying on-premises sizes and permissions into one AWS account preserve the old risk in a harder-to-read bill?
Plain answer
AWS migration services move applications, databases, identity, and operations into a governed Amazon Web Services environment. RaftLabs builds the landing zone, classifies each workload, defines infrastructure as code, rehearses cutover and rollback, and validates production before retirement. A focused first workload starts at $20K and usually takes six to ten weeks.
The first AWS diagram had twenty services and one account.
The team had chosen containers, queues, serverless jobs, and a managed database before deciding who could change production or where audit logs would survive an account incident. The application design looked modern. The operating boundary did not exist.
The landing zone comes before the workload.
Recorded AWS migration delivery
- 300K+
- customer records moved
- Energia Rewards project record
- 12 weeks
- rebuild and migration delivery
- Recorded project duration
- 4
- scheduled customer feeds
- Domestic and commercial joiner and leaver files
The Energia Rewards case study documents a platform migration that used AWS Cognito for first-sign-in identity transfer and processed four scheduled customer feeds. Its 12-week duration and 300K-plus record scope come from retained project records, not an independent audit. The case does not establish a universal AWS migration speed, cost, or architecture.
Choose AWS when the estate and operating team support it, not because its catalogue is longest.
The first workload should test the account model, cost assumptions, recovery path, and handover discipline.
AWS is already selected through existing capability, contracts, services, or a documented platform comparison.
Workload and security owners can approve IAM, network, logging, backup, cutover, and retirement decisions.
The team that inherits AWS can review infrastructure code and own cost, incidents, access, and releases.
The provider decision ignores Microsoft licensing, data-platform needs, residency, or internal operating skill.
The application is near retirement or its main constraint needs product or code change first.
The plan depends on one broad administrator role, one account, and backups inside the same failure boundary.
EC2 rehost vs managed-service replatform
| EC2 rehost | Managed-service replatform | |
|---|---|---|
| Change | Preserve the application runtime | Change selected runtime or data services |
| Use when | Exit deadline and stability lead | A measured operating burden justifies change |
| Acceptance | Functional, performance, recovery, and cost parity | Also compatibility, service limits, and new runbooks |
| Main risk | Old sizing and operations follow the app | Service complexity exceeds team capacity |
Scope
What belongs in an AWS migration release
- 01
AWS assessment and target decision
Inventory workloads and dependencies, model likely consumption, compare provider fit, and state why AWS is the target for this wave. - 02
Landing zone and IAM boundaries
Define accounts, organizations, network paths, identity federation, roles, secrets, central logs, recovery copies, policies, and budgets before workload access opens. - 03
Infrastructure as code
Create reviewed Terraform or an agreed AWS-native equivalent for network, compute, data, permissions, observability, and environment differences. - 04
Application, database, and identity movement
Rehost or replatform only the selected components, reconcile data, preserve login and permission behavior, and test every external dependency. - 05
Cutover and AWS operating handoff
Rehearse traffic switching and rollback, validate production, monitor spend and reliability, then transfer access, runbooks, and change ownership.
How it works
From AWS target design to accepted workload
- Phase 101
Assess workload and AWS fit
Map dependencies, demand, recovery, identity, data, licences, current cost, team skill, and the business reason for AWS.
- Phase 202
Build the landing zone and plan
Define accounts, organizational controls, network, IAM, logging, backup, budgets, infrastructure code, migration path, and wave runbook.
- Phase 303
Migrate and rehearse
Move a representative workload and its data, test integrations and operations, measure target cost, and rehearse cutover and rollback.
- Phase 404
Cut over and transfer
Execute the approved switch, validate production, monitor the workload, transfer runbooks and access, and retire source resources deliberately.
Risk
What the AWS decision record must settle
- Account and permission boundary
- State where production, logs, security tools, recovery copies, and lower environments live and who can change each one.
- Service exit cost
- Record portability and data-egress implications before a managed service becomes part of the application design.
- Recovery independence
- Protect copies and credentials so a mistaken deletion or compromised production account cannot remove the only recovery path.
- Measured target cost
- Revisit sizing, storage, transfer, commitments, and idle resources after the representative workload produces real usage data.
Scope and price
A focused AWS migration starts at $20K.
Start with the landing-zone controls and one representative workload, including data, rehearsal, cutover, validation, and operating handoff.
The first workload proves the AWS pattern and measured run cost before the remaining estate follows it.
Starting investment
Starts at $20K
A focused first workload usually takes six to ten weeks after assessment. Identity change, large databases, hybrid networking, regulated evidence, or several accounts can extend the plan.
Infrastructure is reviewable code
Rollback stays available through acceptance
Related cloud and operations services
- 01
Cloud Migration Services
Vendor-neutral workload classification, wave planning, cutover, and handover.
- 02
Azure Migration
Microsoft estate, Entra identity, licensing, landing-zone, and hybrid migration planning.
- 03
Database Migration
Schema, data, replication, application compatibility, and database cutover.
- 04
DevOps Services
Repeatable delivery, observability, infrastructure change, and incident readiness after migration.
Work with us
Bring the workload and the AWS assumption you have not tested.
Share the dependency map, current cost, recovery need, acceptable downtime, identity model, and operating team. We will scope a representative first move.
- Scope and cost agreed before work starts. No surprises. No obligation.
- Working prototype within 3 weeks of kickoff.
- Pay by milestone. You see progress before each invoice.
- 60-day post-launch warranty. Bug fixes, UI tweaks, and deployment support. No retainer.
- All conversations are NDA-protected.
Frequently asked questions
Straight answers to what buyers ask before they scope. Still stuck? .
They include workload discovery, AWS fit and cost assessment, landing-zone design, account and network controls, IAM, infrastructure as code, application and database movement, identity transition, cutover rehearsal, rollback, production validation, monitoring, documentation, and handover. The exact service choices follow the workload rather than a standard AWS checklist.
Rehost when the deadline and application condition favor minimal change. Replatform when a specific managed service reduces a measured operating burden without forcing a redesign. ECS may suit containerized services, while Lambda may suit short event-driven work. EKS adds an orchestration platform and should have a clear scale or portability case.
The structure depends on team and regulatory needs, but it should separate production from lower environments, centralize audit and security records, define identity and permission boundaries, control network paths, protect recovery copies, apply budgets, and make changes through reviewed code. One shared account is rarely a durable production boundary.
We inventory schemas, queries, users, authentication flows, and recovery needs before choosing RDS, Aurora, self-managed compute, or another target. Data movement uses rehearsed export, restore, or replication with reconciliation. Identity migration includes duplicate handling, recovery paths, session behavior, permission tests, and rollback if the new directory cannot authorize correctly.
A focused first workload starts at $20K and usually takes six to ten weeks after assessment. A complete quote names the landing-zone controls, the infrastructure code, the workload and data in this wave, the identity work, the rehearsal and cutover, the validation, the handover, the period where the old and new environments run side by side, and what is excluded. Any change is priced and approved in writing before the work is done. It covers landing-zone controls, infrastructure as code, one related application cluster, data movement, rehearsal, cutover, validation, and handover. Complex databases, identity changes, hybrid networks, regulated evidence, or several accounts increase scope. The calendar also holds dependency owners settling the map, access and approval windows, the rehearsal, an agreed cutover window, and the source kept running until acceptance completes. Dates slip when an unknown dependency surfaces late, approvals are waited on, or a cutover window is missed.
You own it, from day one. The AWS accounts are opened in your name and under your control from the start, and the infrastructure code, data, runbooks, and decision notes sit in your accounts and repositories throughout, not handed over at the end. Notes are kept current as the work goes, so another team can take over at any point.
You already hold the AWS accounts, the infrastructure code, the data, the runbooks, and the decision notes in your name, so there is nothing to extract and no unlock step. We do not offer source-code escrow, because the estate is already yours throughout.
Penetration testing is taken care of. No production data is used in development, ever; testing runs on made-up data shaped like the real thing. Tested backups are kept throughout, and offboarding steps remove access when someone leaves a team. The AWS services and any other third parties the design sends data to are named in the scope document before signing. The duties that come with your own industry, and the evidence your auditors ask for, stay yours; scoping names which records the target environment holds for those checks. We claim practices we can show you, not certifications.
After acceptance, the workload can be run by your own team from the runbooks and handover notes, carried into a further migration wave, or held under an ongoing engagement agreed in writing. What keeps costing money is the AWS usage itself (compute, storage, and data transfer), the licences that move with the workload, monitoring and backup services, and the old environment until the source is retired. Naming those costs at scoping is part of the quote, so the bill after go-live is not a surprise.
We work on five Remote Work Principles. 01 Switch to Async: decisions and updates are written so nobody waits on a meeting. 02 Be Prepared: calls and cutover windows come with the material read in advance. 03 Write: the migration state is written down, so what has moved, what is rehearsed, and what is waiting on a decision is always readable. 04 Ask and tell: questions and problems are raised early, in writing. 05 Own: each task and each cutover decision has a named owner.
Yes. We sign your NDA before anything sensitive is shared, and the inventory, cost figures, and access details you share in scoping stay confidential. Day-one ownership of the accounts and code is the stronger protection: the estate is in your name from the start.
No. The team that scopes your migration does the work, and the people on your calls are the people on your project. Our team is based in India and Ireland. AWS is the platform the work lands on, not a team your project is handed to.