Azure Migration Services
Azure migration services for Microsoft estates that cannot leave identity, licensing, and hybrid dependencies until cutover.
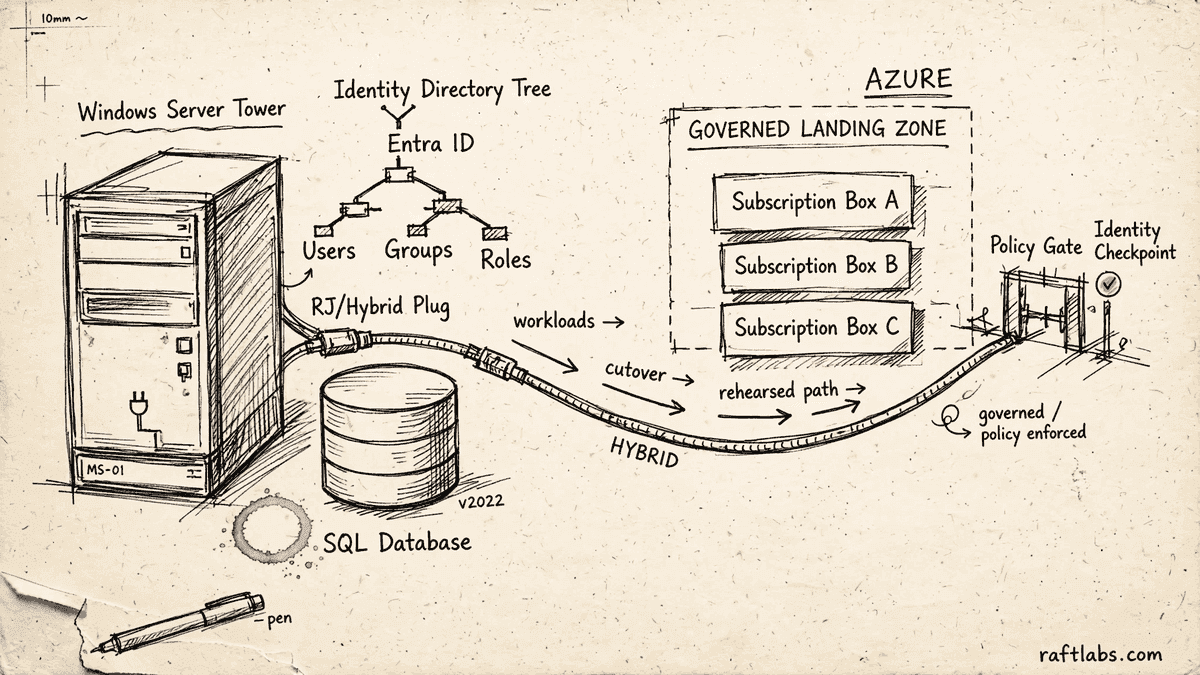
An Azure migration is rarely just a server move. We map Windows, SQL Server, Active Directory, Microsoft 365, network, licence, and application dependencies; build the subscription and policy foundation; test a representative workload; and rehearse the hybrid cutover before production changes.
Bring the problem, the current workflow, or the existing code. We reply with a practical next step within one business day.
The brief
Start with what is not working.
Good software decisions begin with the constraint, not a list of features or a preferred technology.
Is an expiring Windows or SQL Server estate driving a deadline before the licence and identity model is understood?
Would moving virtual machines first leave authentication, Group Policy, file shares, and cross-database jobs stranded on premises?
Plain answer
Azure migration services move Microsoft workloads, databases, identity, and operations into a governed Azure environment. RaftLabs maps Windows, SQL Server, Active Directory, licensing, and hybrid dependencies; builds the landing zone as code; rehearses cutover and rollback; and validates production. A focused first workload starts at $20K and usually takes six to ten weeks.
The server moved. The login path stayed behind.
The application ran on an Azure test VM, but production authentication still depended on an on-premises domain controller and two service accounts nobody had inventoried. The migration rehearsal failed before any customer saw it. That was the useful result.
A Microsoft estate moves as a dependency system.
Adjacent migration delivery
- 300K+
- customer records moved
- Energia Rewards project record
- 12 weeks
- rebuild and migration delivery
- Recorded project duration
- 11
- legacy-data remediation scripts
- Recorded migration scope
The Energia Rewards case study documents a large identity and data migration, but its published implementation is not an Azure case. We use it here only as adjacent evidence for discovery, remediation, identity transition, and staged launch. Its metrics come from retained project records and do not establish Azure-specific performance, cost, or timing.
Choose Azure when the Microsoft estate and future operating model point to it together.
The first wave should test identity, policy, networking, SQL compatibility, recovery, and the real licence position.
Azure is supported by existing Microsoft capability, agreements, services, or a documented provider comparison.
Application and platform owners can approve Entra, network, policy, database, cutover, and source-retirement decisions.
The inheriting team can review infrastructure code and own access, cost, incidents, backup, and releases.
The platform choice rests only on assumed licence savings that nobody has modelled against the actual agreement.
The application is near retirement or needs product and code changes before hosting matters.
The plan leaves identity, DNS, file, or database dependencies on premises without a supported hybrid operating model.
Azure VM vs managed Azure platform
| Azure VM rehost | Managed-service replatform | |
|---|---|---|
| Change | Preserve Windows or application runtime | Adopt App Service, managed containers, or managed data |
| Use when | Compatibility and exit deadline lead | A known operating burden justifies change |
| Acceptance | Function, identity, performance, recovery, cost | Also service limits, compatibility, and new runbooks |
| Main risk | Old sizing and administration follow | Platform constraints surface late |
Scope
What belongs in an Azure migration release
- 01
Microsoft estate and licence assessment
Inventory workloads, support dates, agreements, current rights, identity paths, SQL features, demand, recovery needs, and provider-fit assumptions. - 02
Azure landing zone and governance
Define management groups, subscriptions, policy, Entra roles, network, logs, secrets, backup boundaries, budgets, and resource naming before workload access opens. - 03
Infrastructure as code
Create reviewed Terraform or Bicep for shared controls and workload resources, with environment differences explicit rather than repeated by hand. - 04
Application, SQL, and identity movement
Choose VM or managed targets from compatibility evidence, reconcile migrated data, test Entra and hybrid paths, and preserve rollback until acceptance. - 05
Cutover and Azure operating handoff
Rehearse the switch, validate business and technical checks, monitor production and cost, then transfer runbooks, access, and change ownership.
How it works
From Microsoft estate map to accepted Azure workload
- Phase 101
Assess estate and Azure fit
Map applications, Windows and SQL versions, identity, licences, data, network, recovery, current cost, and team capability.
- Phase 202
Design landing zone and wave
Define management groups, subscriptions, policy, Entra roles, network, logging, backup, budgets, infrastructure code, and hybrid dependencies.
- Phase 303
Migrate and rehearse
Move a representative workload, test identity and data paths, measure target behavior and cost, and rehearse cutover and rollback.
- Phase 404
Cut over and transfer
Execute the approved runbook, validate production, monitor the workload, transfer operations, and retire source resources after acceptance.
Risk
What the Azure decision record must settle
- Identity authority
- State which directory owns each user and service account, how synchronization works, and how administrators recover access.
- Licence evidence
- Model actual agreement rights and support dates instead of applying a headline discount to every workload.
- Hybrid lifetime
- Name which network, DNS, file, identity, and database links remain after cutover and who operates them.
- SQL compatibility
- Test application queries and engine features against the chosen Azure target before data volume makes rollback expensive.
Scope and price
A focused Azure migration starts at $20K.
Start with landing-zone controls and one representative workload, including identity, data, rehearsal, cutover, validation, and handover.
The first workload proves the Azure pattern, licence assumptions, and measured run cost before the remaining estate follows it.
Starting investment
Starts at $20K
A focused first workload usually takes six to ten weeks after assessment. Complex SQL, identity change, hybrid networking, regulated evidence, or several subscriptions can extend the plan.
Licence assumptions are written down
Hybrid dependencies stay owned
Related cloud and operations services
- 01
Cloud Migration Services
Vendor-neutral workload classification, wave planning, cutover, and handover.
- 02
AWS Migration
AWS account, IAM, network, workload, database, and cutover planning.
- 03
Database Migration
Schema, data, replication, application compatibility, and database cutover.
- 04
DevOps Services
Repeatable delivery, observability, infrastructure change, and incident readiness after migration.
Work with us
Bring the Microsoft dependency that makes a simple server move impossible.
Share the Windows and SQL inventory, identity model, licences, hybrid network, recovery need, and downtime limit. We will scope the safest first workload.
- Scope and cost agreed before work starts. No surprises. No obligation.
- Working prototype within 3 weeks of kickoff.
- Pay by milestone. You see progress before each invoice.
- 60-day post-launch warranty. Bug fixes, UI tweaks, and deployment support. No retainer.
- All conversations are NDA-protected.
Frequently asked questions
Straight answers to what buyers ask before they scope. Still stuck? .
They include estate discovery, Azure fit and cost assessment, landing-zone design, subscription and policy structure, Entra identity, hybrid networking, infrastructure as code, application and SQL migration, cutover rehearsal, rollback, production validation, monitoring, documentation, and handover. The service choice follows the workload and operating team.
Azure deserves close consideration when Windows Server, SQL Server, Active Directory, Microsoft 365, Azure DevOps, existing agreements, and internal Microsoft capability shape the estate. Those inputs do not make Azure automatic. Data services, residency, portability, provider concentration, and the future operating model still belong in the comparison.
We inventory users, service accounts, groups, applications, authentication protocols, conditional-access needs, and recovery flows first. The plan states what remains in Active Directory, what moves or synchronizes with Entra ID, how applications change, who can administer each boundary, and how access is tested before production cutover.
The answer depends on engine features, linked servers, agent jobs, cross-database work, CLR use, application compatibility, availability needs, licences, and operating goals. A VM preserves the most control and burden. Managed Instance can reduce change while adding management. Azure SQL Database needs deeper compatibility testing but removes more administration.
A focused first workload starts at $20K and usually takes six to ten weeks after assessment. It covers landing-zone controls, infrastructure as code, one related application cluster, data and identity work, rehearsal, cutover, validation, and handover. Complex SQL estates, hybrid networking, regulated evidence, or several subscriptions increase scope. A complete quote names the landing-zone controls, the identity work, the data to be moved, the system connections, the rehearsal, and what is excluded. Any change is priced and approved in writing before the work is done. Cloud consumption, Microsoft licensing, and third-party tooling remain separate unless a proposal states otherwise.
Not necessarily a long outage. The pattern on this page is a rehearsed cutover: the representative workload moves first, identity and data paths are tested, and the switch follows an approved runbook with a rollback path. The acceptable outage is agreed before the wave is planned, and the rehearsal measures how long the switch actually takes. A plan that needs a long outage window is a plan that has not been rehearsed enough.
You own it, from day one. Your Azure subscriptions, accounts, infrastructure code, data, diagrams, and runbooks are in your name and under your control from the start, not handed over at the end. The operating notes stay current while we work, so another team could continue from them.
You already hold everything. Your Azure subscriptions, accounts, infrastructure code, data, diagrams, and runbooks are in your name and in your hands from day one, and the operating notes stay current while we work, so another team can pick up from them. There is no unlock step and nothing you need to extract from us. We do not offer source-code escrow, because the estate is already yours throughout.
Penetration testing is taken care of. No production data is used in development, ever: testing runs on made-up data shaped like the real thing. Backups are tested, not just scheduled. When someone leaves a team, offboarding steps remove their access. The third-party services the system depends on, including Microsoft services and any tooling that processes your data, are named in the scope document before you sign. We claim practices we can show you, not certifications.
Three arrangements are possible: another fixed phase for the next wave, an ongoing engagement, or your own team running the estate from the diagrams, code, decisions, and runbooks handed over. Whichever you choose, running Azure carries standing costs that exist whoever operates it: cloud consumption, Microsoft licensing, third-party tooling, and monitoring. Those costs are named before you sign, not discovered on the first invoice after go-live.
We work on five principles. 01 Switch to Async: updates are written so you can read them between your own meetings, not saved for a call. 02 Be Prepared: calls come with the material sent ahead, so the time is spent deciding. 03 Write: decisions, dependency findings, and open questions are written down where both sides can find them. 04 Ask and tell: questions and bad news are raised early and in plain words. 05 Own: the person who takes a point owns it to the end. You talk to the people doing the work, and progress is visible as a rehearsed runbook and reviewable code, not status percentages.
Yes. We sign your NDA before anything sensitive is shared, and the inventory, licence, and access details you share in scoping stay confidential. The stronger protection is structural: your subscriptions, code, and data are in your name from day one, so what you share is never the only copy.
No. The team that scopes your migration does the work, and the people on your calls are the people on your project. Our team works from India & Ireland. Microsoft services and third-party tools are systems the work connects to, not a handoff of your project.
Ask for the dependency map before the wave plan: if they cannot show you what talks to what, they cannot plan the cutover. Require a rehearsed rollback runbook with named go and no-go owners. Watch the first workload: it should be a representative workload, not the easiest one. And confirm who runs the Azure estate afterward: you need someone who can resolve problems under stress, not just move servers.