Mobile POS and merchant-acquiring platform
A mobile POS product with one payment ledger across PayBy and Stripe, role-controlled GraphQL access, and payment-event processing.
API Development Services
We design and build custom REST APIs, GraphQL layers, and webhook systems for product teams that need stable contracts between applications. The work includes authorization, failure handling, versioning, observability, and usable documentation, not just a set of endpoints that works in a demo.
Bring the problem, the current workflow, or the existing code. We reply with a practical next step within one business day.
Trusted by



The brief
Good software decisions begin with the constraint, not a list of features or a preferred technology.
Are integrations slowing down because every consumer interprets the same data differently?
Do API changes reach production before documentation, permissions, and failure paths are ready?
Plain answer
API development services design and build the contracts applications use to exchange data and actions. RaftLabs delivers REST APIs, GraphQL layers, and webhook systems with authorization, versioning, failure handling, tests, observability, and documentation. The first release is scoped around one bounded domain and the consumers that depend on it.
The first consumer gets a response and the integration looks finished. Then a request is retried, a field changes, a token has the wrong scope, or a downstream system times out after completing the request. Without a written contract for those cases, every consumer invents its own workaround.
A dependable API makes ownership and failure explicit. It tells consumers what they may send, what they can expect back, how changes are introduced, and what happens when part of the transaction fails.
If the left side fits, custom development may be sensible. If the right side fits, use the vendor connector or managed backend first.
Several applications or partners need a stable interface to the same business capability.
Authorization, audit history, retries, or versioning carry real operational risk.
The underlying business rules do not fit a standard connector or managed backend cleanly.
A supported connector already covers the data and actions you need.
The source system and ownership rules are still changing every week.
You need a one-time data transfer rather than a maintained interface.
Scope
Resources, queries, commands, and events reflect real consumer jobs. Schemas, validation, pagination, errors, and examples use consistent conventions so a second integration does not require a second interpretation.
Authentication proves identity; authorization controls what that identity may read or change. We model roles, scopes, tenant boundaries, and sensitive fields against the business domain, then test denied paths as carefully as allowed ones.
Webhook signatures, idempotency keys, retry policies, dead-letter handling, and replay tools prevent duplicate or delayed events from silently corrupting state. Operators can see which event failed and what happens next.
OpenAPI or schema documentation lives with the implementation. Contract tests catch incompatible changes. Metrics, traces, logs, rate limits, and an ownership runbook make the API supportable after launch.
| Pattern | Use it when | |
|---|---|---|
| REST | Resource operations over HTTP | Consumers need predictable commands and broad tooling support |
| GraphQL | A typed query layer | Clients need different views of a connected domain |
| Webhooks | Event delivery to a consumer endpoint | Another system should react without polling |
| Batch or files | Scheduled bulk exchange | Volume matters more than immediate response |
The choice is not ideological. A product may expose REST for commands, GraphQL for a complex interface, and webhooks for downstream events. We keep each pattern narrow enough to explain and operate.
REST is a dependable default when consumers need predictable resource operations and broad tooling support. The contract still needs more than routes and verbs: an OpenAPI review, consistent status and error semantics, bounded pagination, object-level authorization, and evidence that a deprecated field can be removed without surprising consumers. Mutating requests also need idempotency that follows the downstream business step, not only the HTTP request.
GraphQL fits when several clients need different connected views of the same domain. It is usually unnecessary for a simple single-client CRUD interface. A production GraphQL layer needs resolver batching to prevent N+1 work, query-depth or cost limits, field-level authorization, schema deprecation, and traces that expose expensive operations. Federation should follow a real ownership boundary; adding it before domains and teams are stable creates another coordination layer without solving a buyer problem.
Delivery
Design the boundary before code makes it expensive to change.
Define who calls the API, which system owns each field, and what the first bounded domain must do. We record throughput, latency, compliance, and availability constraints without pretending every endpoint needs the same service level.
Agree resources, events, permissions, error responses, idempotency rules, and versioning. Consumer examples and a contract review expose ambiguity before implementation begins.
Implement the interface, contract tests, authentication, rate limits, retries, monitoring, and documentation. Tests cover duplicates, partial failure, timeouts, and forbidden access as well as successful requests.
Onboard the first consumers, watch latency and errors, document operational ownership, and support the production handoff. New consumers and domains follow only after the first contract holds up in use.
Proof
A mobile POS product with one payment ledger across PayBy and Stripe, role-controlled GraphQL access, and payment-event processing.
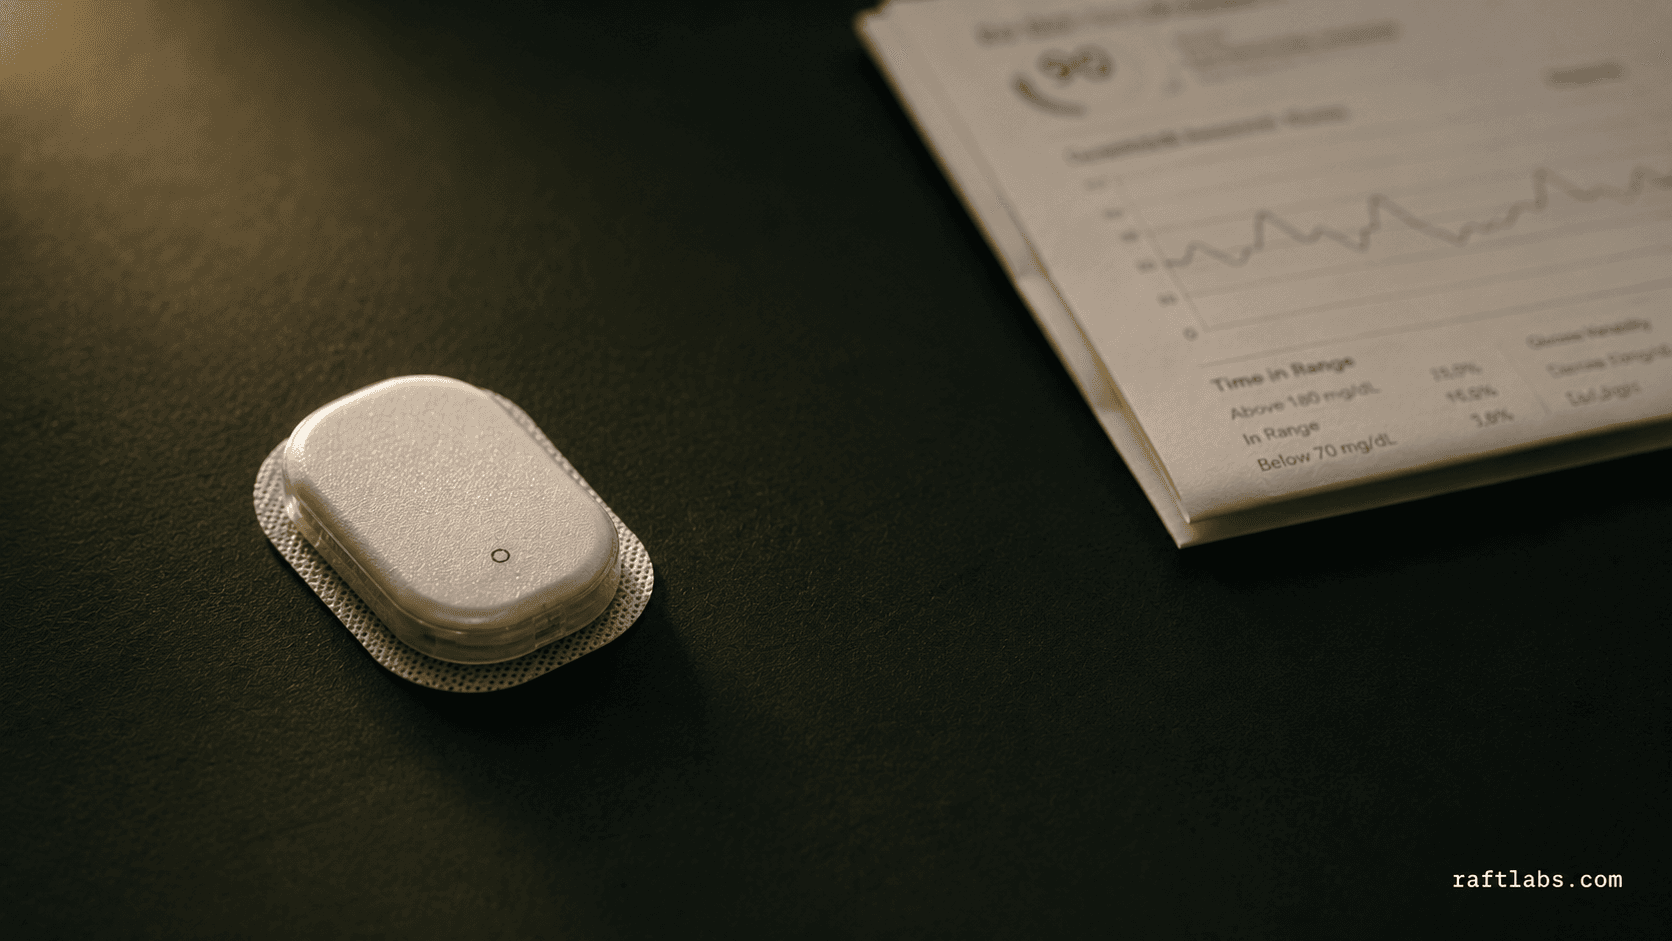
AI integration in the remote patient monitoring app lifts efficiency by automating data analysis and providing personalized insights through wearable health monitoring devices such as CGM and BPM. This advancement has cut clinical decision-making time by 20%, enabling virtual care management, particularly in chronic care scenarios.
A US healthcare client needed more than video calls. We built Galen, a nurse-assisted HIPAA-compliant telehealth platform where a clinic nurse operates diagnostic peripherals while a remote doctor directs via body diagram and issues e-signed prescriptions. In-person visits dropped 60%. Patient engagement increased 30%. 50+ clinics onboarded in 12 weeks.
Bring the consumer journeys, sample payloads, current failure examples, and security constraints. We will determine whether the right first step is a custom API, a supported connector, or a narrower interface change, then define the smallest production boundary worth building.
Work with us
We will map its consumers, ownership, and failure paths, then show you the smallest API release worth building.
A production API engagement includes contract design, implementation, authentication and authorization, validation, consistent errors, versioning, automated tests, documentation, monitoring, and a release plan. Webhooks also need signature verification, retries, idempotency, and a visible path for failed events.
REST is a strong default for resource-based operations and broad interoperability. GraphQL helps when different clients need different views of the same domain. Webhooks notify another system when an event occurs. Many products use more than one pattern, but each should solve a specific consumer need.
Yes, if the legacy system exposes a dependable database, file, procedure, or interface. An API layer can create a safer boundary for new consumers, but it does not remove unreliable data or hidden business rules underneath. We identify that boundary before recommending an API-only approach.
Version the URL, publish a deprecation timeline, and avoid removing or renaming anything inside a supported version. Versioning is a promise-keeping problem: every breaking change needs a migration path and a communication plan for the clients that depend on the old behaviour. Design the first version as if the second already exists.
The endpoints are the smallest part of the budget. Authentication that survives a security review, versioning, documentation, rate limiting, monitoring, and operational tooling are where the budget lives. An internal API costs a fraction of a partner API, which costs a fraction of a public one: the audience determines how much rigor each layer needs.
Ask any vendor about the specific failure classes: service keys shipped in browser bundles, unprotected routes, user identity taken from the caller instead of the session, and unsigned webhooks. The answers should be boring and specific: key rotation, server-enforced authorization on every route, signed webhook payloads, not a general promise of security.
You do. The code, specifications, keys, and infrastructure live in your accounts with work-for-hire IP transfer at each milestone. Insist on standard protocols and a real data export from day one: a custom query language with no export is a rewrite waiting to happen.
Read the documentation as if you were a new developer: can a competent outsider integrate without emailing anyone? Ask for a live test environment and try the core calls yourself. Require the supplier to demonstrate versioning, rate limiting, and error handling, not just the happy path. Good docs are the difference between an API people use and one they ask about.
The main scope drivers are the number of business domains and consumers, authorization depth, event volume, regulatory controls, legacy dependencies, and the stability of upstream data. We define the smallest contract that can serve real consumers and be operated safely before expanding it.