AI Prototype Audit
Find out what your AI-built prototype is hiding before customers do.
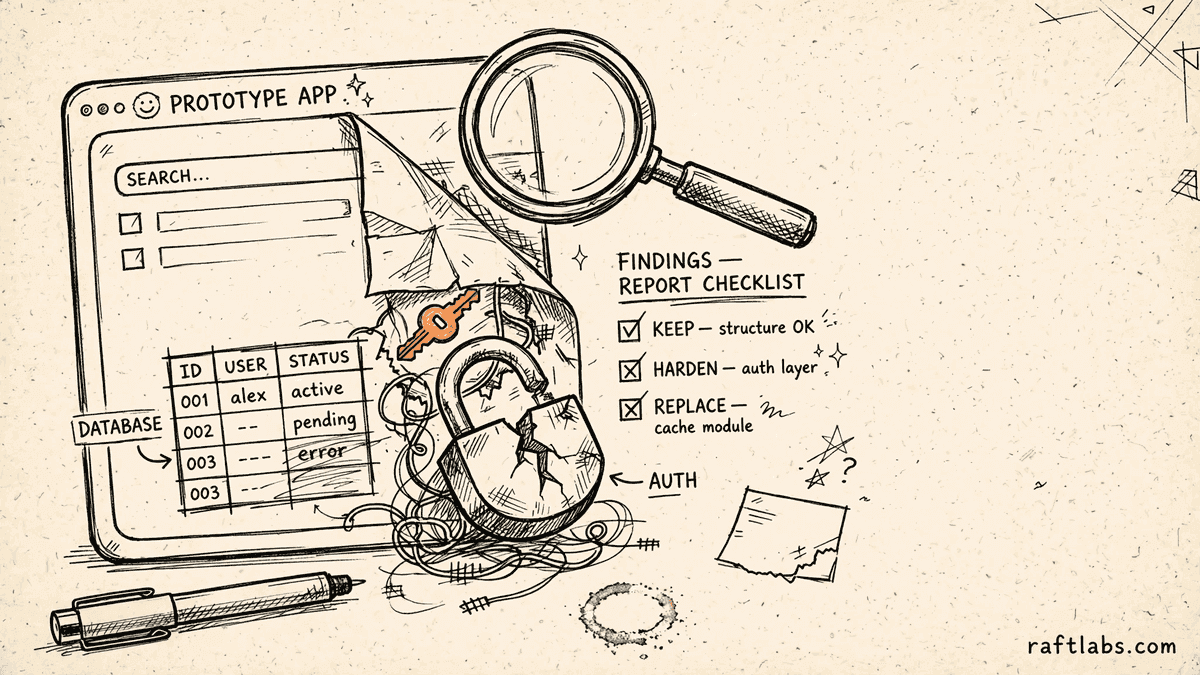
A fixed one-to-two-week diagnostic for prototypes built in Lovable, Replit, v0, Bolt, or similar tools. We inspect the invisible foundation, including the auto-created database schema, authentication, security posture, secrets handling, and integrations, and deliver a written findings report: what can stay, what must be hardened, what should be replaced, and what can wait. No obligation to continue.
Bring the problem, the current workflow, or the existing code. We reply with a practical next step within one business day.
The brief
Start with what is not working.
Good software decisions begin with the constraint, not a list of features or a preferred technology.
You said "yes" when the tool asked to persist data. Now a database exists that you never designed and cannot explain.
Nobody on your team can answer basic questions: who can see whose data? What happens when two users edit the same record? Where are the API keys stored?
Investors, partners, or enterprise prospects are asking about security, and you have no answers.
Plain answer
An AI prototype audit is a one-to-two-week diagnostic that inspects the hidden foundation of a prototype built in Lovable, Replit, v0, or similar tools: database schema, authentication, authorisation, secrets handling, integrations, and deployment safety. RaftLabs delivers a written findings report grading each part keep, harden, replace, or defer, plus a fixed-scope plan for production hardening.
The most expensive question is the one nobody asked.
"Do you want to persist this data?" You said yes. A database was created, tables inferred, an API generated. It felt like magic because the decisions were made for you, invisibly.
Those invisible decisions are now load-bearing: the schema shapes every query you will ever write, the auth model decides who can see what, the secrets handling determines your breach surface. An audit makes every one of them visible, graded, and priced to fix before a customer, a partner, or an attacker asks the question for you.
Audit facts
- 1-2 weeks
- fixed diagnostic window
- Repository access required
- 5 areas
- data, identity, secrets, integrations, operations
- Every finding graded and ranked
- Yours
- the report stays with you
- No obligation to continue
When the audit pays for itself
Real users, customer data, payments, or a security questionnaire are approaching, and you cannot answer foundation questions today.
You need a fixed, evidence-backed scope before committing budget to production work.
A technical decision-maker (you, a co-founder, or an advisor) can grant repository and environment access.
The prototype is still an experiment and no real data or users are near; keep iterating.
You already operate the system in production and need a penetration test or compliance audit instead.
Repository and environment access cannot be shared; without it, an audit is guesswork.
From audit to production
The audit is step one of the prototype-to-production journey. Step two, production hardening, implements the report: real schema, real auth, security controls, integrations, and a safe launch. Fixed scope, agreed after the evidence is in.
Work with us
Know what is inside the build before customers find out.
One to two weeks, a written report, and a fixed scope for whatever comes next.
- Scope and cost agreed before work starts. No surprises. No obligation.
- Working prototype within 3 weeks of kickoff.
- Pay by milestone. You see progress before each invoice.
- 60-day post-launch warranty. Bug fixes, UI tweaks, and deployment support. No retainer.
- All conversations are NDA-protected.
Frequently asked questions
Straight answers to what buyers ask before they scope. Still stuck? .
A written findings report covering the data layer, identity, secrets, integrations, and operations. Every finding is graded keep, harden, replace, or defer, ranked by risk, with a fixed-scope and fixed-price proposal for the hardening phase. The report is yours whether or not you continue with us.
No. The audit is a standalone diagnostic. Many teams use the report to prioritise their own engineering; others engage us for the hardening phase. Either way you leave with evidence instead of guesses.
The prototype tool project (or exported repository), the database, environment configuration, and a walkthrough of the product with someone who knows what it should do. Without repository and data access we cannot audit, and we will tell you that upfront rather than guess.
A penetration test attacks a running system to find exploitable vulnerabilities. The audit is broader and earlier: it assesses whether the foundation (schema, auth model, data isolation, operations) can carry a production product at all. If you already have a production system, you likely want a pentest; if you have a prototype approaching production, you want this first.
Yes. The audit inspects the build in front of us regardless of how it was produced. No-code tools create the same class of invisible-foundation problems, and conventional prototypes often carry the same demo-grade shortcuts.
The audit is a fixed-price engagement, agreed in writing before it starts, so the price never depends on what the audit finds. This page publishes no starting figure because the price follows the size of the build in front of us: one prototype, its database, and its connected services. A complete quote names what is inspected (the data layer, sign-in and access, secrets and connected services, and operations), what you receive (the written findings report and the fixed-scope hardening proposal), what is excluded, who owns the code and accounts, the price, the timing, and what 'done' looks like agreed in writing. A change is priced and approved before the work happens, never added to the invoice after.
One to two weeks, once access is in place. The calendar holds more than reading code. It holds checking how user data is separated, testing what a signed-in user can actually reach, tracing where keys and credentials live, and writing findings you can act on without us in the room. Dates slip when repository or database access waits, or when the walkthrough with someone who knows the product cannot be scheduled. The parts you control are access, the walkthrough, and how fast you answer questions about what the product should do.
You do, from day one. The code, the repositories, and the project notes are yours. The prototype tool project, the database, cloud, payment, and other provider accounts the product runs on are in your name, so you hold the logins and the billing relationship. The findings report is yours whether or not you continue with us. Nothing is handed over at the end because you held it throughout.
You already hold everything a new team needs: the code, the repositories, the accounts in your name, your data, and the written findings report, which grades every part keep, harden, replace, or defer so another team can work from it directly. There is nothing to extract from us, no unlock step, and no fee to leave. That holds whether you move by choice or because we stop trading.
Penetration testing is taken care of before launch. No production data is used in development, ever, so real customer data never sits in a test system. Backups are tested, not just scheduled. When someone leaves a team, offboarding steps remove their access. The third-party services the product depends on, including the database and hosting platform, payment providers, and any AI providers that process your data, are named in the scope document before you sign. We claim practices we can show you, not certifications.
The legal obligation is yours. It attaches to your industry and to the data your product handles, such as customer accounts and payments. The audit checks the technical controls that support it, such as who can see and change each record, how access is separated between users, and what happens to customer data if something fails. Your own operations, agreements, and evidence complete it. Compliance is shared, and we never call a product compliant until the technical, operational, and legal requirements are all verified.
After the audit you choose: your own team works from the report, another team works from it, or we carry out the hardening phase under the fixed scope the report sets out. Running the product also carries standing costs that exist whoever built it: hosting and database plans, payment provider fees, monitoring and error tracking, and updates when a provider or platform changes its rules. Scoping names those categories for your product, so the running cost is part of the decision, not a surprise after launch.
We work on five Remote Work Principles. 01 Switch to Async: most updates are written, so you can read and reply in your own time. 02 Be Prepared: calls come with the material in advance, so the call itself decides things. 03 Write: decisions and progress are written down where both sides can find them. 04 Ask and tell: questions and problems are raised as soon as they appear, not held for a status meeting. 05 Own: the person working on a piece owns its outcome and says so plainly. You talk to the people doing the work, and the findings report is the shared record of what was found.
Yes. We sign your NDA before anything sensitive is shared, and the details you share for the audit stay confidential. The NDA is the first protection, not the strongest one. The stronger protection is in the contract: the code, accounts, and data are yours from day one, in writing.
No. The team that scopes your audit is the team that carries it out, and the people on your calls are the people reading your build. Our teams are in India & Ireland. If a specialist service is needed, such as a payment processor or a database platform, that is a connection your product uses, named in the scope, not a handoff of your project.