"The collaboration was very well managed from start to finish."
James Foskin
Founder & CEO, TiAiMe Limited
Prototype to Production Services
Lovable, Replit, v0, and similar tools take you from idea to working demo in days, but the generated foundation (a hidden Supabase database, no real schema, no auth model, no security review) was never meant for paying customers. We take the prototype you already validated and rebuild its foundation for production: proper data architecture, authentication, security, integrations, and operations, without losing what made the demo work.
Bring the problem, the current workflow, or the existing code. We reply with a practical next step within one business day.
The brief
Good software decisions begin with the constraint, not a list of features or a preferred technology.
The demo works, but you have no idea what is happening under the hood. The database, the auth, and the data model were all created for you, invisibly.
The moment real customers arrive, bringing concurrent users, real payment data, and support tickets, the prototype starts falling apart.
You know exactly what you want the product to do, but the underlying structure cannot carry it.
Plain answer
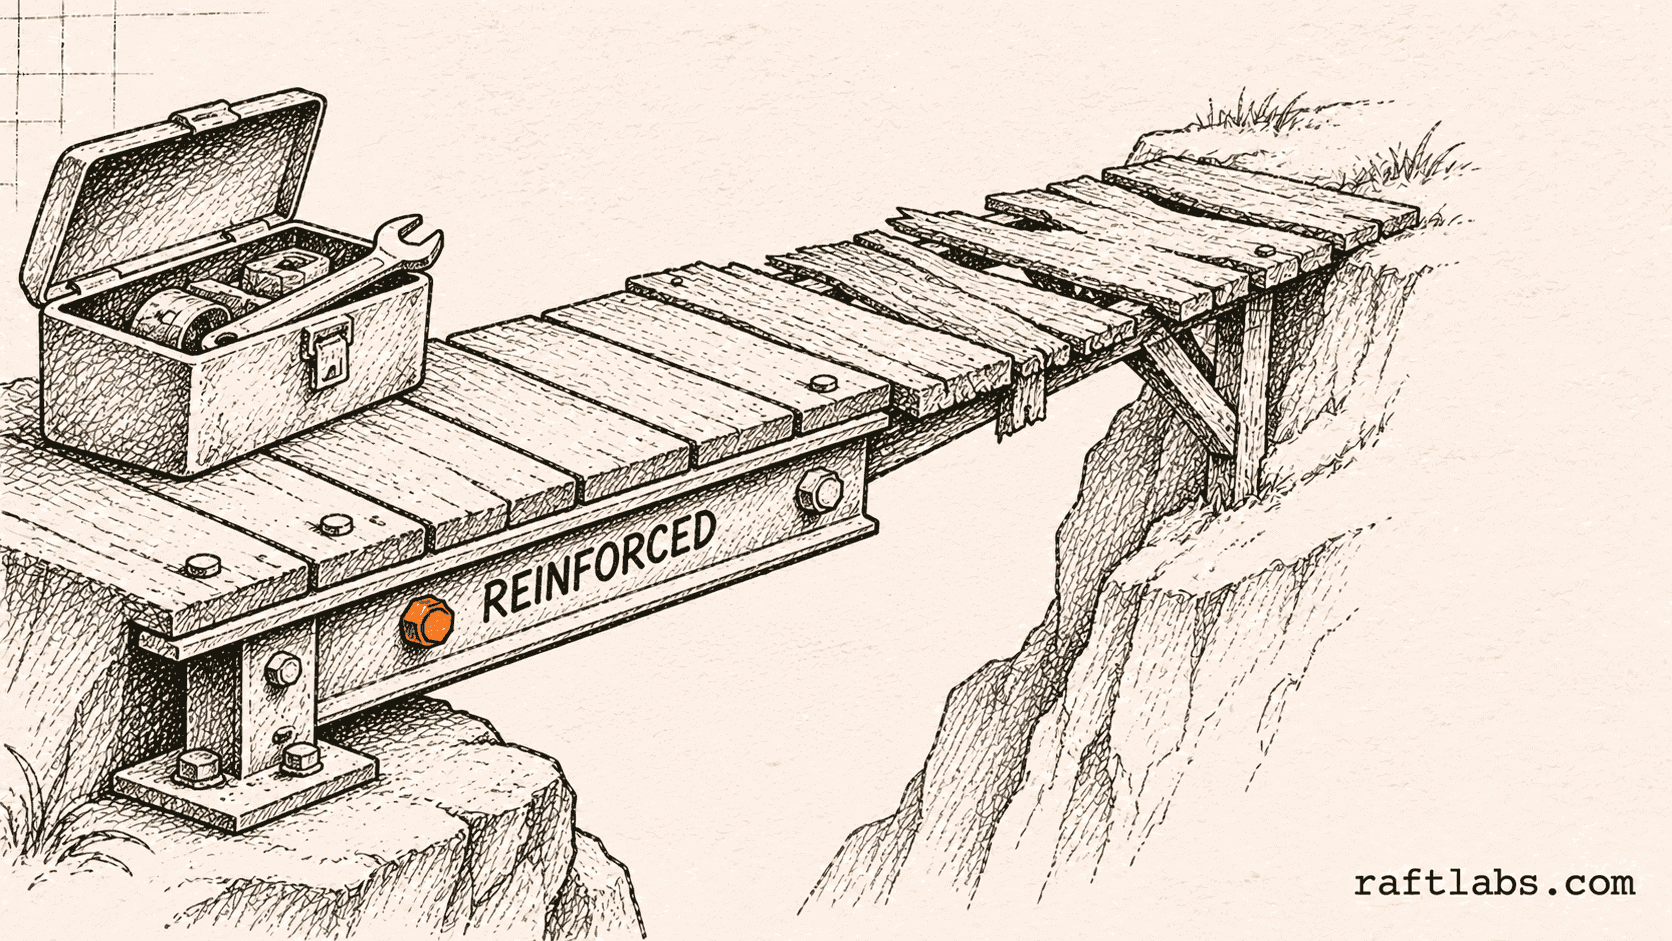
Prototype-to-production services take an AI-built prototype (Lovable, Replit, v0, Bolt) that validated an idea and rebuild its foundation for real customers. RaftLabs audits the generated database schema, authentication, security, and integrations, then hardens or replaces what cannot carry production load while keeping the validated product experience intact.
What to remember
When you clicked "persist this data" in Lovable, a Supabase database appeared. You never designed a schema; the tool inferred one. Authentication exists, but there is no model of who may see or change what. It works beautifully for one person clicking the happy path.
Real customers change every assumption: separate accounts with separate data, concurrent writes to the same records, expired sessions, retried payments, webhooks arriving twice, a dependency failing at 2 AM. None of that was in the demo, and the generated foundation has no answers for it. That is not a flaw in the prototype; it did its job, which was validating the idea. Production is a different job.
Delivery facts
You validated the idea; users, stakeholders, or revenue signal say the product should exist.
The prototype was built in Lovable, Replit, v0, Bolt, Base44, or similar, and you cannot see or explain its foundation.
Real customers, real data, payments, or business continuity are now on the line.
You can provide repository access, the prototype tool project, and a product owner who can make keep-or-change decisions.
You are still testing whether the idea itself makes sense; keep iterating in the prototype tool.
You need one known defect fixed on an already-operating production system.
You want a production guarantee without repository access, a security review, or an agreed definition of what 'done' looks like.
1. AI prototype audit: A one-to-two-week diagnostic. We inspect the generated database, auth, security posture, integrations, and deployment, then deliver a findings report: what can stay, what must be hardened, what should be replaced, and what can wait. Fixed scope, fixed price, no obligation to continue.
2. Production hardening: The build phase. We implement the audit's recommendations: real schema, real auth, security controls, integrations, observability, and a safe launch. Fixed scope agreed after the audit, never quoted blind.
Explore the audit · Explore production hardening
| Need | Best fit | Boundary |
|---|---|---|
| Validated product experience | Keep the product, rebuild the foundation | Product experience usually stays; data layer, auth, and operations usually change |
| Whole prototype discarded | Full rewrite | Discards validated product with the broken foundation and adds migration risk |
| Part replaced only when repair leaves unacceptable risk | Audit then harden | Replace a part only when repair leaves unacceptable security, data, or operational risk, documented why |
How we work
A one-to-two-week diagnostic. We inspect the generated database, auth, security posture, integrations, and deployment, then deliver a findings report: what can stay, what must be hardened, what should be replaced, and what can wait.
We implement the audit recommendations: real schema, real auth, security controls, integrations, observability, and a safe launch. Fixed scope agreed after the audit, never quoted blind.
Scope and price
Focused production hardening after a one-to-two-week audit, when one product journey can be made production-ready without a broad rebuild.
We never quote the build blind; the price follows the evidence.
Starting investment
Starts at $20K
The audit is a fixed one-to-two-week engagement; the fixed production scope follows the audit findings.
Never quoted blind
We never quote the build blind; the price follows the evidence.
Proof
Three-year average engagement. Founders and operators describing the work in their own words. No marketing varnish.
RaftLabs has been an exceptional partner. From the start, they became more than just a service provider, they embraced our vision with their expertise and dedication. We're proud of the result.
Jennyfer Ngueno
CoFounder & CEO, Sekou
"The collaboration was very well managed from start to finish."
James Foskin
Founder & CEO, TiAiMe Limited
Work with us
We will inspect the hidden foundation, surface the production gaps, and give you a fixed scope for making it real.
Straight answers to what buyers ask before they scope. Still stuck? .
Yes, that is exactly who this service is for. These tools are excellent at validating ideas quickly. The problem is never the idea or the interface; it is the invisible foundation (auto-created database, flat schema, demo-grade auth) that cannot carry real customers. We keep the validated product and rebuild what sits underneath it.
Because a demo exercises one happy path with seeded data. Production adds concurrent users, stale sessions, retries, failed payments, webhook duplicates, support escalations, and deploys while the system is running. Prototype scaffolding typically has no schema constraints, no tenant isolation, no rate limiting, and no observability, so the first real load exposes all of it at once.
Not by default. A rewrite discards the validated product along with the broken foundation, and adds migration risk. Our audit separates the two: the product experience usually stays, while the data layer, auth, and operations usually change. We replace a part only when repair would leave unacceptable security, data, or operational risk, and we document why.
The repository and generated services, the database schema and constraints, authentication and authorisation, secrets and credential handling, third-party integrations, data isolation between users or tenants, error handling and retries, deployment and rollback safety, and what happens to customer data if something fails. The deliverable is a findings report plus a fixed production scope.
Focused production hardening starts at $20K, after the audit. The audit is a fixed one-to-two-week engagement, and focused hardening starts around that figure when one product journey can be made production-ready without a broad rebuild. We never quote the build blind; the price follows the evidence. A complete quote names the product journey in scope, the database and sign-in model, the security controls, the payment and provider connections, what is excluded, who owns the code and accounts, the price, the timing, and what 'done' looks like agreed in writing. A change is priced and approved before the work happens, never added to the invoice after.
Bug fixing assumes a production system with known defects. Your prototype is not a production system yet; it lacks the schema, auth model, security posture, and operational footing that bug fixes take for granted. We build that footing first; then normal maintenance applies.
The audit takes one to two weeks. The hardening timeline is set in the fixed scope that follows it, because the calendar depends on what the audit finds. The calendar holds more than building. It holds designing the real database and sign-in model, moving your data across safely, testing security and payments, and a staged rollout to a first group of real customers. Dates slip when repository or provider access waits, when a payment or platform approval sits outside the build, or when the scope changes mid-build. The parts you control are access, decisions, and how fast you review each stage.
You do, from day one. The code, the repositories, and the project notes are yours. The prototype tool project, the database, cloud, payment, and other provider accounts the product runs on are in your name, so you hold the logins and the billing relationship. Handover notes stay current during the build, so another team could continue from them. Nothing is handed over at the end because you held it throughout.
You already hold everything a new team needs: the code, the repositories, the accounts in your name, your data, and handover notes kept current during the build. There is nothing to extract from us, no unlock step, and no fee to leave. That is the structural answer to the question, and it holds whether you move by choice or because we stop trading.
Penetration testing is taken care of before launch. No production data is used in development, ever, so real customer data never sits in a test system. Backups are tested, not just scheduled. When someone leaves a team, offboarding steps remove their access. The third-party services the product depends on, including the database and hosting platform, payment providers, and any AI providers that process your data, are named in the scope document before you sign. We claim practices we can show you, not certifications.
The legal obligation is yours. It attaches to your industry and to the data your product handles, such as customer accounts and payments. The build carries the technical controls scoping names, such as who can see and change each record, a history of what changed, and how long records are kept. Your own operations, agreements, and evidence complete it. Compliance is shared, and we never call a product compliant until the technical, operational, and legal requirements are all verified.
After launch you can continue with another fixed phase, an ongoing engagement, or your own team working from the handover notes and runbooks. Launch also starts standing costs that exist whoever runs the product: hosting and database plans, payment provider fees, monitoring and error tracking, and updates when a provider or platform changes its rules. Scoping names those categories for your product before you sign, so the running cost is part of the decision, not a surprise after launch.
We work on five Remote Work Principles. 01 Switch to Async: most updates are written, so you can read and reply in your own time. 02 Be Prepared: calls come with the material in advance, so the call itself decides things. 03 Write: decisions and progress are written down where both sides can find them. 04 Ask and tell: questions and problems are raised as soon as they appear, not held for a status meeting. 05 Own: the person working on a piece owns its outcome and says so plainly. You talk to the people doing the work, and progress is visible as working software at the end of each build cycle.
Yes. We sign your NDA before anything sensitive is shared, and the details you share for the audit stay confidential. The NDA is the first protection, not the strongest one. The stronger protection is in the contract: the code, accounts, and data are yours from day one, in writing.
No. The team that scopes your product is the team that builds it, and the people on your calls are the people on your project. Our teams are in India & Ireland. If a specialist service is needed, such as a payment processor or a database platform, that is a connection your product uses, named in the scope, not a handoff of your project.
Yes. AI is part of the workflow in everything we do, from testing to writing code, and that work runs through RaftKit, our own AI workflow process at raftkit.com. The concern behind the question is the right one on this page: your prototype was AI-built, and unchecked generated code is how the hidden foundation problems started. RaftKit runs in five phases, Blueprint, Plan, Build, Review, and Compound, and each phase has quality gates the work must clear. Review happens in two stages, first checking the work matches what was asked, then a wider review from several angles. Findings carry a severity, and a serious (P1) finding blocks the work from shipping. A named person stays accountable for what ships.